01
Sovereign Systems Architecture
Private, custom operating software engineered around how your company actually functions. No shared multi-tenant clouds leaking client records, no brittle vendor integrations, and zero proprietary lock-in.
 KOVA OS
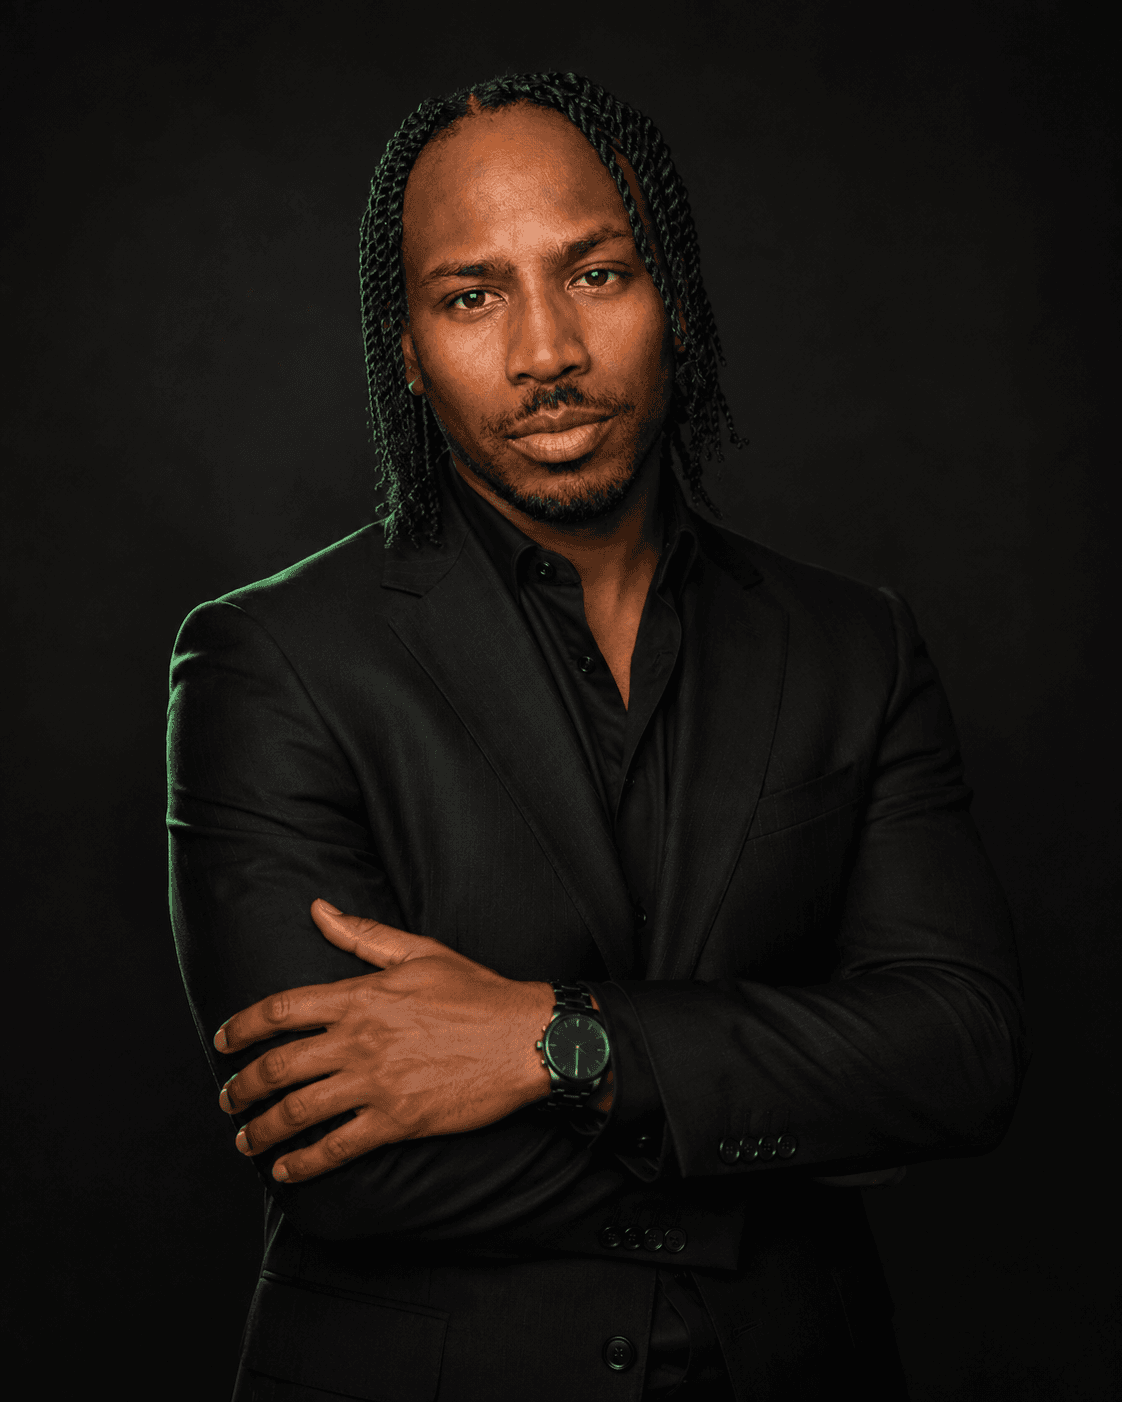
“Bring us the dream. Bring us the nightmare. We’ll help you turn it into a system.”
I am an operator and principal software engineer based in Chicago, Illinois. I started Kova OS to solve a specific problem: brilliant, hardworking business owners getting ground down by operational friction.
When you run a growing business, your craft is rarely what slows you down. What exhausts you is the drag around the edges: missing customer inquiries while you are in the field or up on a job, hunting through text threads for a quote sent three weeks ago, wrestling with disjointed software tools, and sitting at the kitchen table at 10 PM doing work that should have run itself.
My job is to engineer order out of that reality. I do not sell abstract roadmaps or delegate code to offshore subcontractors. I personally architect every system, write deterministic software, and ensure you hold 100% of the cryptographic keys and code repositories.
When operations get messy, the conventional advice is always to buy more software. Owners sign up for another subscription, bolt on another third-party app, and suddenly find themselves managing five separate logins that do not talk to each other. The tools end up creating more administrative drag than the original bottleneck.
Kova OS approaches this as an engineering discipline. We isolate the operational spine of your company, strip out unnecessary software, and build one private operating system engineered around how you actually work. You own the repository, the database, and the infrastructure.
While building operational software for Chicago firms, I uncovered an alarming vulnerability: small business domains were routinely left undefended against spoofed email. Fraudsters were sending fraudulent wire instructions and fake invoices directly from legitimate-looking company addresses.
Default internet email protocols permit anyone to put your business domain in a message header. To protect our clients, I created Kova Shield—an uncompromising domain defense protocol built around RFC 7208 (SPF), RFC 6376 (DKIM), and RFC 7489 (DMARC). We enforce strict policy rejection without ever asking for or touching client passwords. You keep total control; your perimeter stays closed.
I hold a firm stance on client sovereignty: your company should never be held hostage by a software vendor. Every repository we code is created in your GitHub organization. Every database is provisioned under your account. Every DNS record is documented in a permanent Shield Record. If you ever decide to part ways, your software continues running smoothly without interruption.
Private, custom operating software engineered around how your company actually functions. No shared multi-tenant clouds leaking client records, no brittle vendor integrations, and zero proprietary lock-in.
Architect of Kova Shield. Protecting businesses, title companies, and practices against domain impersonation, wire fraud, and forged emails under the strict Zero-Password Protocol.
Deterministic DNS implementation of RFC 7208 (SPF), RFC 6376 (DKIM), and RFC 7489 (DMARC). Strict policy enforcement (p=reject) ensuring fraudulent messages are stopped before reaching customer inboxes.
Engineering automated intake pipelines, structured customer databases, event dispatchers, and custom executive portals written in TypeScript, Next.js, and Postgres.
Photographed in Chicago. High-resolution reference portraits for editorial, press, and a consistent public profile.
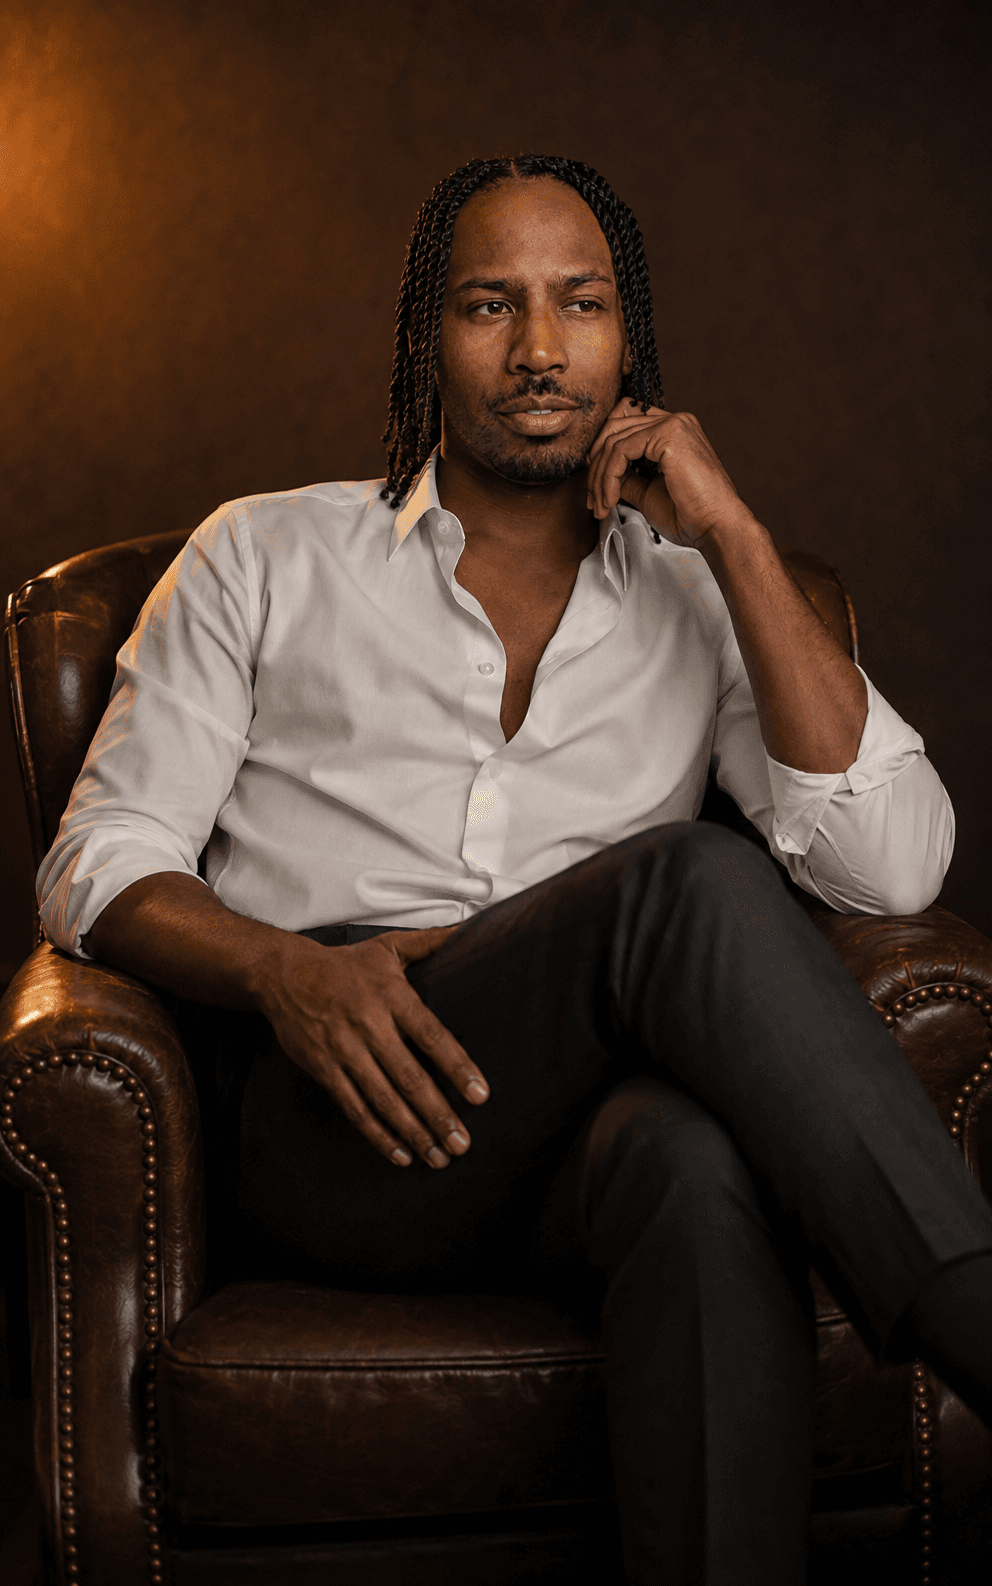
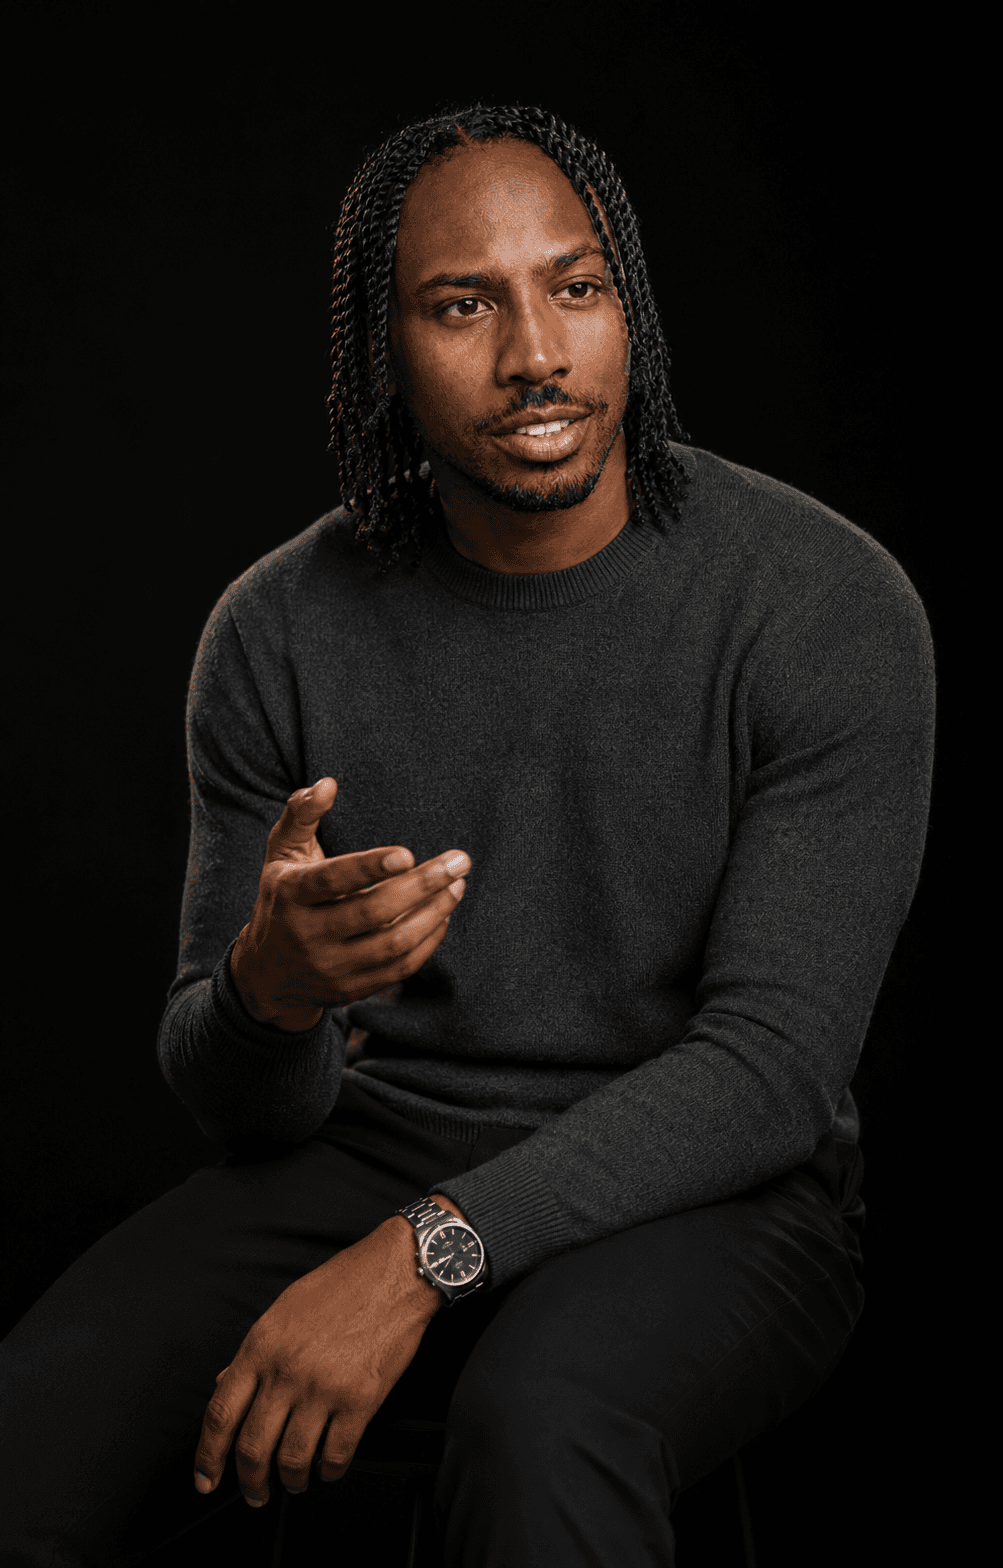
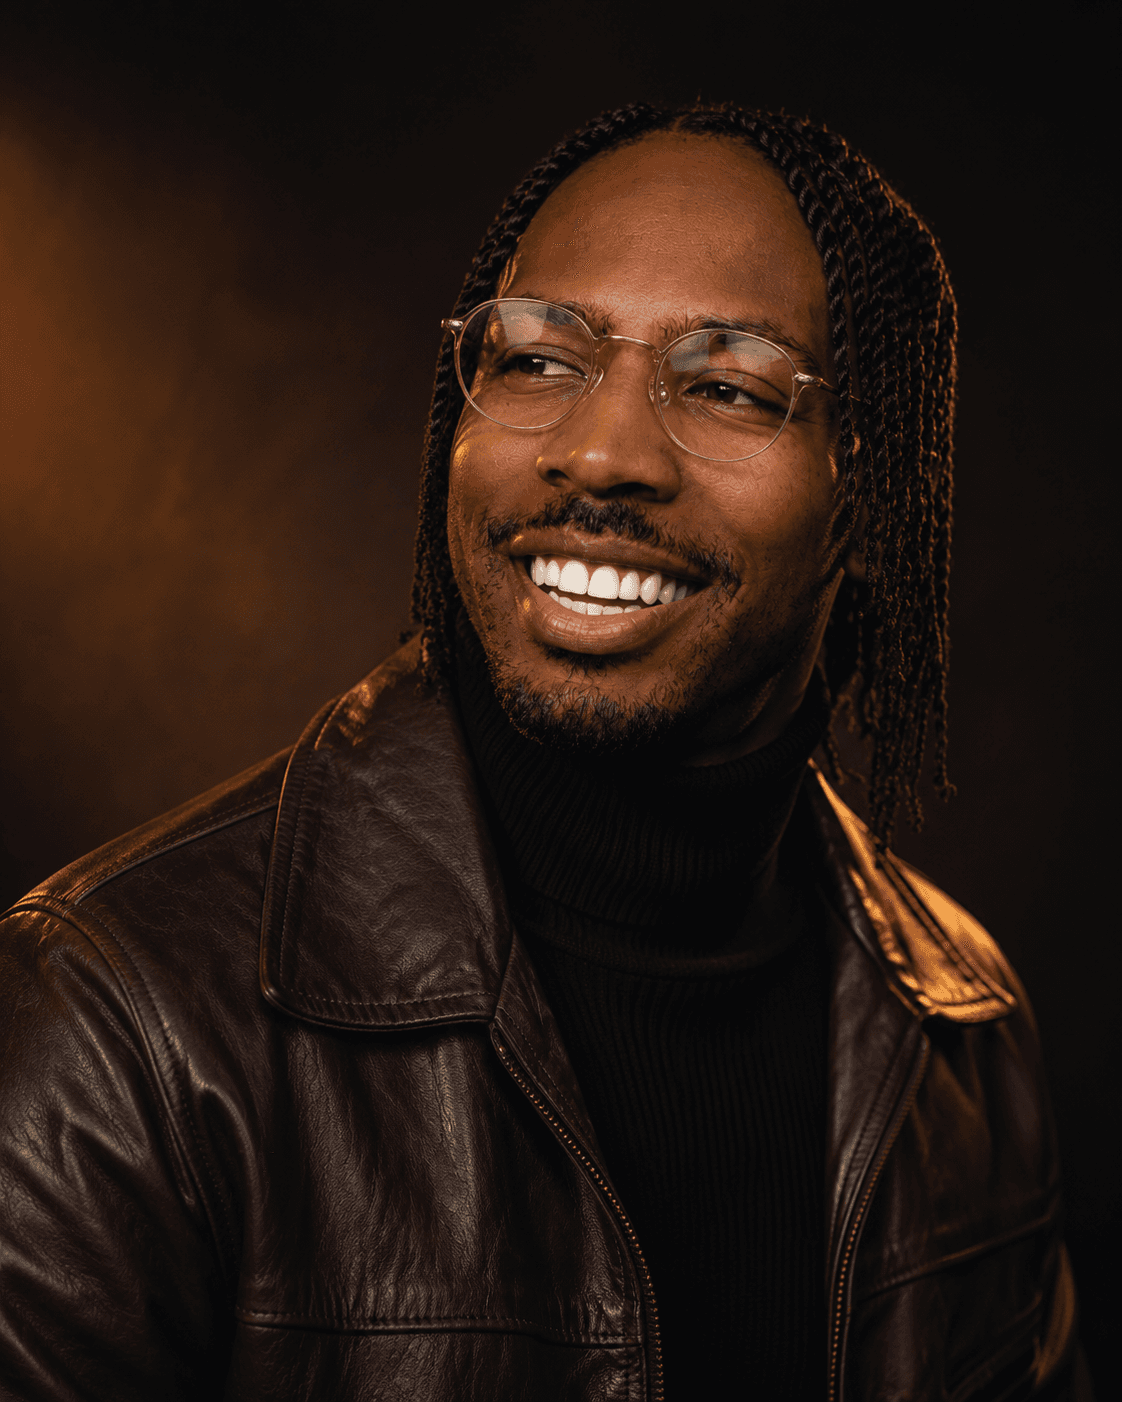
Official digital footprints, public source repositories, and corporate registry entries for Alphonzo Cirton and Kova OS.
Submit your intake in 3 minutes. I personally review your reality, audit your bottlenecks, and write your custom systems roadmap within 48 business hours.